Governance, Risk & Compliance

From initial assessment to audit day and beyond.

Governance, risk and compliance controls surrounding a protection shield

We turn compliance from burden to an asset.

Businesses rarely answer to just one framework.

Most are juggling CMMC, NIST, SOC 2, and PCI DSS at once, each with its own controls, evidence, and deadlines.

Osiris runs GRC as a continuous program, not a scramble before audit day.

We implement the controls, generate the evidence, and fit it all to your frameworks, your industry, and your risk profile.

Governance

Is the structure behind your decisions: who has authority to make them, how they get documented, and how you prove that to a client, an auditor, or a court if you ever have to. Without it, decisions live in someone's head instead of your process.
Risk

Is identifying what could hurt your business before it does. That means a system with no backup, a vendor with access they shouldn't have, or a process that only one person understands. Risk management isn't about eliminating every threat. It's knowing which ones matter and having a plan ready before they hit.

Compliance

Is proof. It's the documentation, policies, and controls that show you meet the standards your industry, your clients, or the law require, whether that's CMMC, HIPAA, ITAR, or a cyber insurance policy. Compliance isn't a one-time checklist. It's an ongoing state you maintain and can demonstrate on demand.

Benefits of GRC

Compliance with Confidence

GRC keeps your organization aligned with the rules that actually apply to your business, industry, and clients.

That means the right policies are in place, the right documentation exists, and you can prove it when someone asks. So when an audit lands or a client wants proof, you're not scrambling.

You're already covered, and it's one less thing that can take your business down.

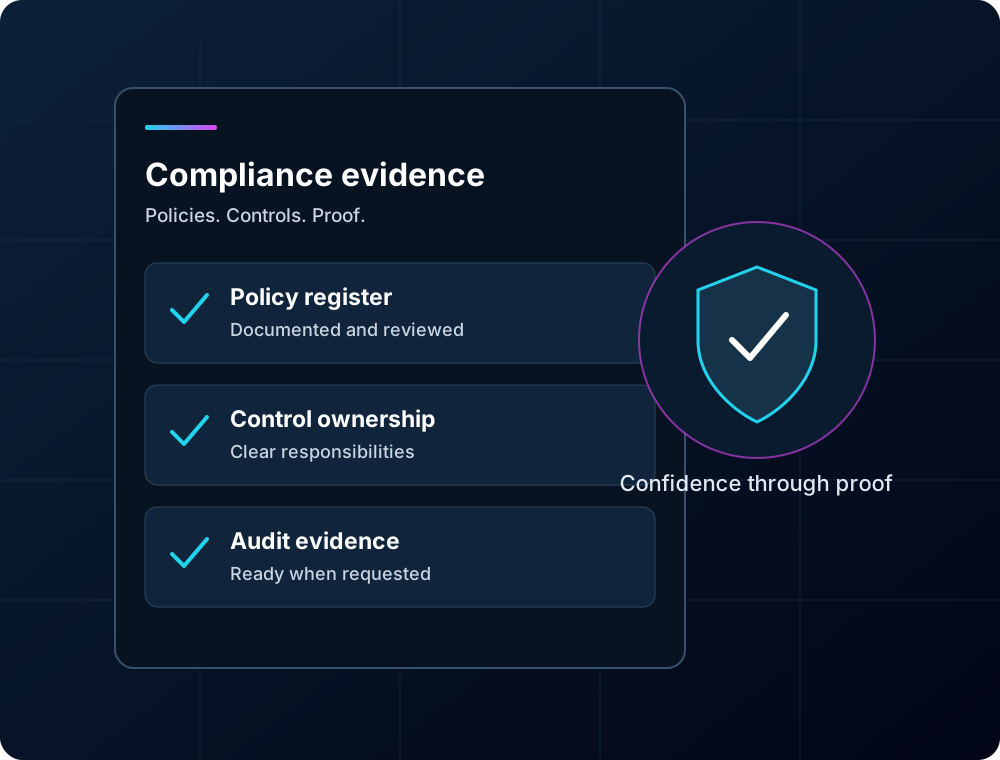
Compliance records with policies, documented controls and audit evidence
Security and digital protection

Protect Your Reputation

A breach or a compliance failure doesn't just cost money. It costs trust, and trust is hard to win back once it's gone.

A solid GRC program protects your data, your systems, and your name. Clients stick around when they know you take this seriously, and it's one more reason they choose you over a competitor who can't say the same.

Make informed decisions

GRC gives you a clear, honest picture of where your risks and compliance gaps actually sit.

Not guesses, not what you assumed last year. What's true right now. That's what lets you make real decisions. Where to spend, what to fix first, what can wait.

Instead of hoping nothing breaks, you know exactly what you're dealing with, and you decide from there

Analytics and risk visibility dashboard

Our Process

Risk Assessment

We identify risks, weigh their likelihood and impact, and decide how each gets handled. The result feeds a risk register, a living record of each risk, its owner, and its status, reviewed and updated as things change, not filed away after the initial assessment.

Governance & Ownership

Every control has a named owner. When something needs attention, there's no question who handles it.

Control Framework Map

Full documentation of every in-scope control, its objective, and the evidence proving it works. One control often covers multiple frameworks, so nothing gets built twice.

Policy & Procedure Development

Policies set the rule. Procedures explain how it's followed. We write both to match how your business actually runs.

Vendor Risk Management

A breach at your vendor becomes your problem. We evaluate the security and compliance posture of every third party with access to your systems or data, and keep the required agreements in place

Evidence Collection

Configs, logs, access records, and screenshots, collected continuously throughout the audit period and organized for fast auditor review.

Change Management

System changes are authorized, tested, and approved before they reach production, and mapped back to the controls they affect.

Logical Access

User access is provisioned, reviewed, and revoked on a set schedule. Privileged accounts get extra scrutiny.

Incident Management

Clear procedures for detecting, responding to, and resolving incidents, with escalation paths and notification requirements defined in advance.

Business Continuity

Backup procedures and recovery plans, tested on a schedule, not just written down and filed away.

Continuous Monitoring

Controls are checked on an ongoing basis, not once a year. Drift gets caught and fixed before it becomes a finding.

Remediation

A failed control gets fixed, tested, and signed off, not logged and left

Audit Support

When audit day comes, your evidence and documentation are already organized and ready to hand over.

Don't Let Compliance Gaps Cost You Contracts.

We'll review your current posture, flag gaps across your required frameworks, and show you what a managed GRC program looks like for your business.

Review My Compliance Posture →

Compliance Is a Program, Not a Project

Most businesses treat compliance like a once-a-year exam. Pass it, forget about it until next time.

That leaves you exposed the other eleven months. It means scrambling for evidence at the last minute. And it does nothing to actually lower your risk.

Osiris runs your compliance program every day of the year, not once a year. Controls are monitored continuously. Evidence gets collected automatically. Gaps get flagged as they appear, not after the fact. Your leadership gets a heads-up before a problem becomes an audit finding.

So when audit season comes around, you're ready. Not because you pulled an all-nighter finding proof, but because the proof was already there.