Security awareness training:
Most breaches involve a human element. Regular training, phishing simulations, and clear reporting procedures build the habits that technical controls alone cannot create
One protects a checklist. The other protects Your Business
These are not edge cases reserved for large enterprises. They are the day to day reality for organizations of every size.
46%
of cyberattacks are reported to target
smaller businesses, according
to industry research.
Most operate without a dedicated
security function.
200 days
is how long
the average breach has to run
before it is caught.
Technology alone does not solve this. Staying ahead of these threats takes expertise, visibility across your entire environment, and the ability to act quickly when something goes wrong
Cyber threats don't clock out. Neither do we.
Shaped by years in enterprise security, we bring that same level of discipline and structure to businesses of every size.
Threat monitoring, incident response, and structured operations, built the way larger organizations run them, without the cost or complexity of building that team inhouse.
Schedule a no obligation call with one of our experts.
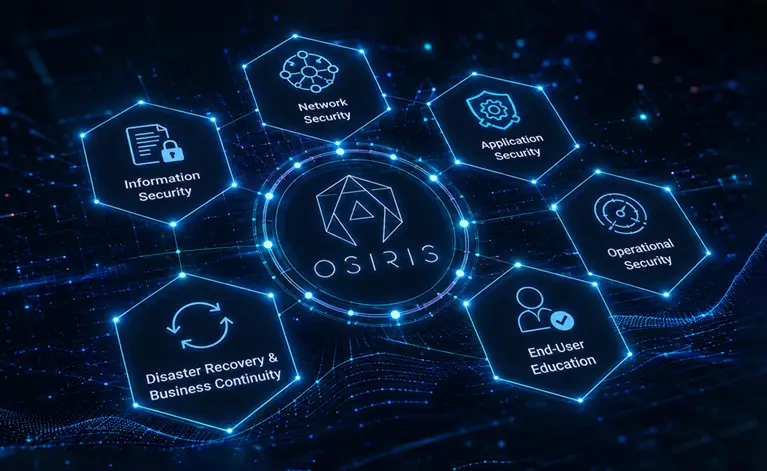
Contact usSecurity only holds when people understand it. At Osiris, we build practical, layered protection and invest in user education so security becomes a natural part of how your business runs
Most breaches involve a human element. Regular training, phishing simulations, and clear reporting procedures build the habits that technical controls alone cannot create
Documented and enforced policies around passwords, data handling, and acceptable use set the baseline for how people operate day to day. Policies without enforcement are decorative.
Known vulnerabilities are publicly listed and actively exploited. Regular patching closes those doors. The window between a vulnerability being published and it being targeted is getting shorter.
Multi-factor authentication, least privilege access, and regular access reviews. Identity is the most commonly exploited entry point and the most consistently overlooked.
A flat network where everything can reach everything gives an attacker freedom to move. Segmentation means a compromise in one area does not automatically become a compromise everywhere.
Every connected device is a potential entry point. Disabling unused services, enforcing encryption, and controlling what can run on each device reduces the available surface area.
Default configurations are publicly documented and frequently exploited. Hardening your setup and removing default credentials are among the highest value steps a business can take.
You cannot protect what you cannot see. A current inventory of every device, application, and service in your environment is the foundation everything else sits on.
A supplier with weak security can become your problem without any direct attack on your own systems. Vendor assessments and monitoring third party access are a necessary part of managing your overall exposure.
Administrator accounts are high value targets. Separating privileged from standard access, requiring additional authentication, and logging all elevated activity limits what a compromised credential can do.
Knowing what data you hold, where it lives, and who can reach it. Encryption, data loss prevention controls, and clear retention policies limit what an attacker can actually take even if they get in.
Prevention includes being ready to respond. Documented plans, defined roles, and tested procedures established before they are needed. Organizations that have rehearsed their response consistently fare better.
Immutable backups cannot be altered, encrypted, or deleted — even by someone with admin access. When ransomware locks your systems, an immutable backup is what gets you back on your feet without paying. It is the one copy an attacker cannot touch